PINSECURITY / VCISO & AI SECURITY
Security and compliance for teams building with AI.
I’m Sara Wolpin, a fractional CISO. I help startups and small businesses get ready for SOC 2, HIPAA and ISO 27001, secure the apps they build with AI tools, and use ChatGPT, Claude and Copilot without leaking data.
$ pin scan --target your-business
Mission: explore every zone and finish the challenges to earn XP and 7 badges.
WHO I WORK WITH
Who I work with.
SaaS startups
SaaS startups facing their first SOC 2 request.
Vibe-coded apps
Founders shipping apps built with Lovable, Cursor or Bolt.
AI at work
Small businesses using ChatGPT, Claude or Copilot that need rules for it.
Healthcare
Healthcare and health-tech teams under HIPAA.
THE EXPERTISE BEHIND PINSECURITY
Hi, I’m Sara Wolpin.
I’m a cybersecurity consultant and the founder of PinSecurity. I’ve led security as a CISO and as a vCISO, and I still like being hands-on. I take risks that feel complicated and turn them into clear steps your team can act on.
Tap a card to run the command ↑
PINSECURITY / CONSULTING
Cybersecurity consulting services.
Here’s what I do. Pick one service or combine a few. Tap a pin on the map to see what each one covers.
Tap a pin · follow the trail from 01 onward
FREE RESOURCES
Free resources.
Four free downloads for your team, from PinSecurity and PinForge. Enter your email, confirm it, and the download starts.
 PINSECURITY · FREE PDF
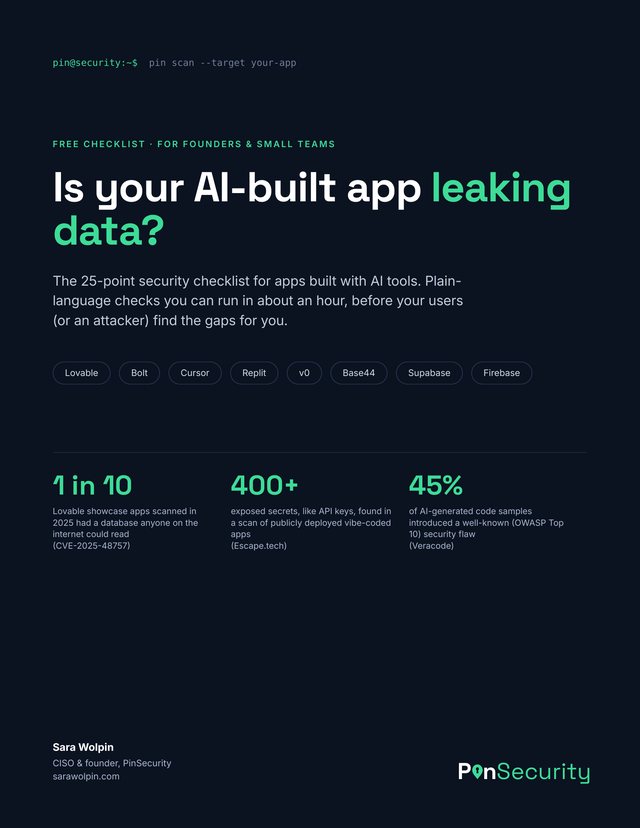
AI-Built App Security Checklist
25 checks for vibe-coded apps built with Lovable, Bolt, Cursor, Replit or Claude Code, from the database to launch.
Get the checklist →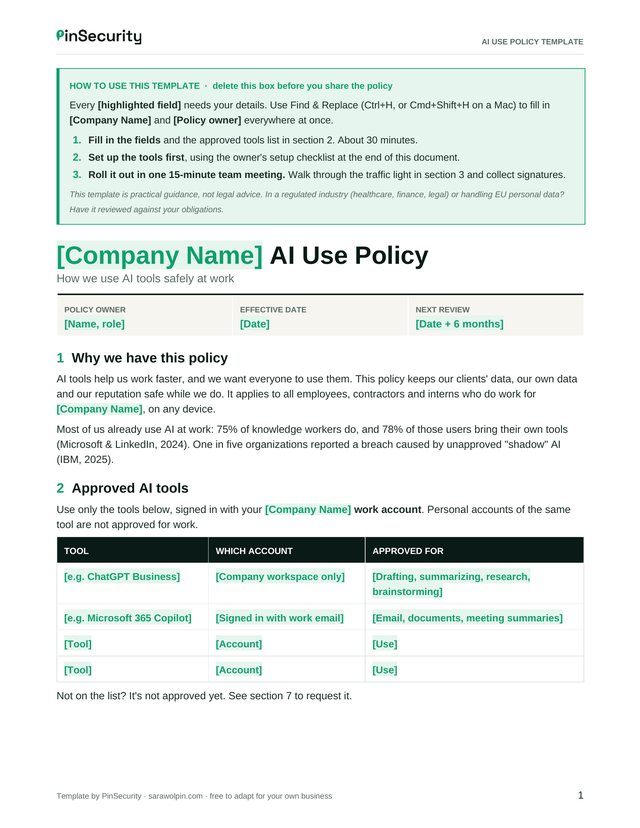 PINSECURITY · FREE WORD TEMPLATE
AI Use Policy Template
An editable policy that tells your team which AI tools to use and what data can go into them.
Get the template →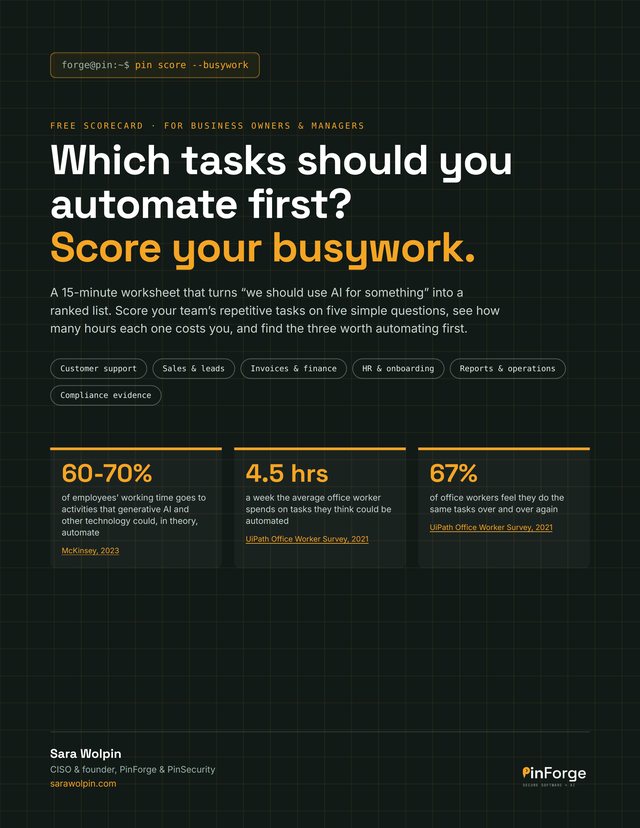 PINFORGE · FREE PDF
AI Automation Scorecard
Score your team’s repetitive tasks on five questions and find the three worth automating first.
Get the scorecard →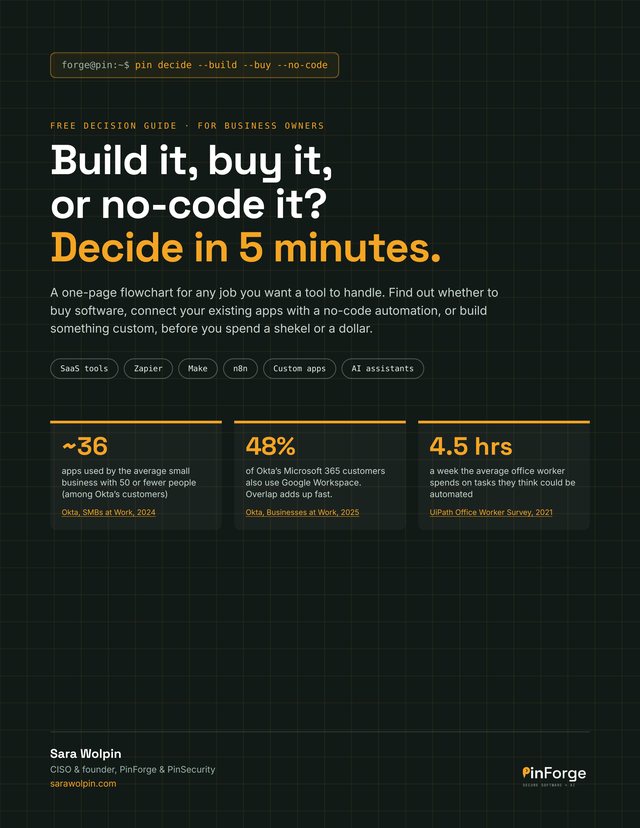 PINFORGE · FREE PDF
Build, Buy or No-Code? Guide
A one-page flowchart to decide whether to buy software, use a no-code automation or build something custom.
Get the guide →HOW IT WORKS
How working with me works.
A free 10-minute call
You tell me where you are and what’s pushing you, like a customer asking for SOC 2, an audit or a launch.
A clear plan and quote
What I’ll do, how long it takes and what it costs, in plain language.
We do the work
A one-off project or ongoing vCISO support. You always know what comes next.
PINFORGE / CUSTOM SOFTWARE + AI
Custom software and AI automation, built securely.
PinForge is my software business. It builds custom software and AI automations, like internal tools, assistants and integrations, so your team spends less time on repetitive work. Every build gets threat modeling, code review and testing before launch.
Free for business owners: the AI Automation Scorecard and the Build, Buy or No-Code? guide.
Custom software
Web apps, portals and internal tools shaped around how your team actually works.
AI agents & assistants
Assistants that answer, draft, sort and summarize, grounded in your own data, with guardrails.
Workflow automation
Connect the tools you already use and remove the copy-paste work between them.
Security built in
Threat modeling, secure code review and testing before launch, done by a security team.
What could AI automate in your business?
Pick the areas that eat your team’s time.
Your automation blueprint will appear here.
FROM SARA’S NOTEBOOK
Security insights.
 WEBSITE SECURITY
PHP2Shell: What Small Business Website Owners Need to Do Right Now
Two critical PHP flaws put most business websites at risk. How to check if your site is affected and the 5 steps to take today.
Read article → SECURE DEVELOPMENT
How to Choose a Secure Outsourced Development Team: Key Questions to Ask
Outsourcing software development can be a game-changer for businesses, providing access to expert talent, faster delivery, and cost savings. But here’s the catch:…
Read article → WEBSITE SECURITY
Stay One Step Ahead - A Beginner’s Guide to WordPress Security
WordPress powers over 40% of the web, making it the go-to platform for millions of websites. However, its widespread popularity makes it a prime target for hackers.…
Read article → SMALL BUSINESS SECURITY
Not Sure If Your Business Needs Cybersecurity? Here's what you should know.
For small and medium businesses (SMBs), cybersecurity often feels like a luxury rather than a necessity. Many owners think, "Why would anyone target us? We're too…
Read article →THE SECURITY ARCADE
Think like a defender.
Three quick challenges. Each one earns XP and a badge. Beat your best score.
An AI assistant wrote this API in seconds. It works, and it has 3 security holes. Tap the vulnerable lines.
QUESTIONS, ANSWERED
Frequently asked questions.
What does PinSecurity do?
PinSecurity is Sara Wolpin’s cybersecurity consulting business. Sara helps companies find and fix security gaps and get ready for audits and regulators. The services are risk assessments and pen testing, AI security and governance, security reviews of AI-built apps, cloud and Microsoft 365 / Google Workspace hardening, gamified awareness training, vCISO and GRC, ISO 27001, compliance readiness (SOC 2, HIPAA, NYDFS), and incident response and forensics.
What is a vCISO (fractional CISO), and what does GRC mean?
A vCISO (also called a fractional or virtual Chief Information Security Officer) is a senior security leader who works with you part-time, for a fraction of the cost of a full-time CISO. GRC means governance, risk and compliance. In practice that’s the security roadmap, policies, risk register, vendor risk and control reviews, and keeping your evidence up to date month after month. At PinSecurity, vCISO and GRC are one service.
Who is PinSecurity for?
Businesses that want practical security help without hiring a full-time security person. For example, teams using ChatGPT, Claude or Copilot at work, founders shipping apps built with Lovable, Cursor or Bolt, SaaS and service companies getting ready for SOC 2, healthcare teams that need HIPAA security, and companies that need ISO 27001 to win bigger clients or enter new markets.
Is my app built with Lovable, Cursor or Bolt secure?
Not by default. These tools build working apps fast, but they can leave a database open to the public, API keys in the front-end code or weak login rules. An AI-built app security review checks logins, database rules, exposed keys and prompt-injection risks before real users and data arrive.
How do I stop employees leaking data into ChatGPT?
Start with a written AI use policy that says which AI tools are approved and what data can go into them. Then use business plans and settings that keep your data out of model training, and turn on data-loss controls in Microsoft 365 or Google Workspace. Sara sets this up as part of AI security and governance.
What does ISO 27001 certification involve?
ISO 27001 certification means an independent certification body has audited your information security management system (ISMS) against the ISO/IEC 27001 standard. First you build the ISMS: you set its scope, run a risk assessment, choose controls to treat the risks, check them against the list in the standard’s Annex A, and record your choices in a Statement of Applicability. Before the audit, you run a full internal audit and a management review. The certification audit has two stages: Stage 1 checks that your ISMS is designed and ready, and Stage 2 checks that it works in practice. A certificate from an accredited certification body is valid for three years, with surveillance audits in between and a recertification audit at the end.
Which compliance frameworks can PinSecurity help with?
Sara helps companies get ready for SOC 2, HIPAA and ISO 27001. For ISO 27001 she helps build an information security management system (ISMS) and prepare for the certification audit. Readiness work starts with a gap analysis, then the controls, policies and evidence you’re missing. She also helps DFS-licensed firms with the NYDFS cybersecurity regulation (23 NYCRR 500).
What does PinForge build?
PinForge is Sara Wolpin’s secure custom software and AI automation business. It builds web apps, portals and internal tools, AI assistants that work from your own data, and automations that connect the tools you already use. Every build gets threat modeling, secure code review and testing before launch.
Can PinSecurity help when something goes wrong?
Yes. PinSecurity writes incident response plans, runs tabletop exercises and gives hands-on help when something goes wrong. Sara’s digital-forensics training (the EC-Council CHFI course) helps her trace what happened and close the gap.
Do you work with clients outside Israel?
Yes. Sara works with clients worldwide.
How do I get started?
Book a free 10-minute call with the button on this page, send a message through the contact form, or message Sara on WhatsApp. She replies to messages within one business day. After the call, she sends a clear plan and a quote.
LET’S MOVE FORWARD
What are you building next?
Tell me what you’re working on or what’s worrying you. I’ll get back to you within one business day. For PinSecurity consulting and PinForge builds.
Jerusalem, Israel · clients worldwide